Binance Hit by the Largest Crypto Hack in History: A Complete Timeline of the $6.3 Billion Security Incident
#Binance #CryptoHack #BlockchainSecurity
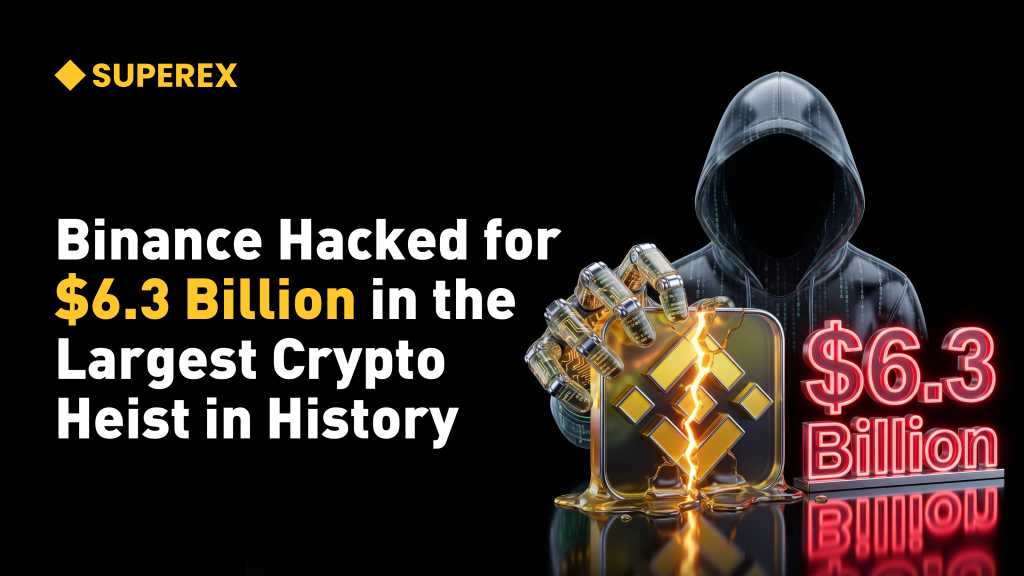
BREAKING: World’s largest crypto exchange Binance hacked with over $6.3 billion stolen:
• $1.45 billion $BTC
• $875 million $ETH
• $234 million $TRX
• $50 million $XAUT
• $1.57 billion $USDT
• $823 million $USDC
• $75 million $WBETH
• $88.5 million $RLUSD
+ $447.5 million additional cryptocurrencies This is the largest hack in crypto history.
On October 30, 2026, Binance officially confirmed a major security incident with an estimated total impact of approximately $6.3 billion. Around $3 billion in affected assets has so far been frozen on-chain.
Binance’s preliminary investigation suggests that the incident may have originated from a compromised laptop belonging to a DevOps engineer. The attacker reportedly gained access to a service container and submitted unauthorized withdrawal transactions. Binance has found no evidence that wallet private keys were directly leaked.
Binance has temporarily suspended deposits and withdrawals, revoked the affected address authorization, and engaged law enforcement agencies, stablecoin issuers, and blockchain security firms to trace the funds. The exchange said all losses would be covered by the SAFU fund and company funds and that user funds remain safe.

Now, let’s walk through the entire incident, step by step.
October 28: The Attacker Begins Preparations
According to on-chain analysis by Web3 security company Blockaid, the attacker began receiving initial funding through Tornado Cash on October 28.
The attacker subsequently tested the complete authorization, delegation, and fund-sweeping process on three self-controlled wallets. Each test moved only $2 to $6, apparently to confirm that the attack process functioned as intended.
October 29, 23:59 Beijing Time: Malicious Sweeper Contract Deployed
At 15:59 (UTC) on October 29, the attacker deployed an unverified smart contract.
The contract was capable of transferring specified tokens and ETH from an authorized wallet and sending the assets to an address controlled by the attacker.
The primary receiving address was: 0x5227f603C1eE34CE3C06eFe6477003BDfCCB2f8c
Etherscan later labeled this address as being associated with the Binance hot-wallet exploit.
October 29, 20:20(UTC): The Attacker Submits 50 EIP-7702 Authorizations
At 20:20:59(UTC) on October 29, the attacker submitted an EIP-7702 transaction targeting “Binance 14,” one of Binance’s primary Ethereum hot wallets.
The transaction contained 50 authorizations covering 50 different nonce values. Because Binance 14 was still processing normal withdrawals, the attacker could not determine its exact current nonce and therefore submitted a batch of possible values.
One authorization eventually matched, delegating Binance 14 to the attacker’s sweeper contract.
20:24(UTC): Approximately $2.5 Billion Transferred in One Transaction
Approximately three minutes and 24 seconds after the authorization became effective, the attacker called the sweeper contract and transferred the following assets from Binance 14:
- Approximately 167,464 ETH;
- Approximately 1.615 billion USDT;
- Around 60 other ERC-20 tokens.
The transaction was worth approximately $2.5 billion at the time. Binance 14 was left with only around 1 ETH after the sweep. Blockaid Technical Analysis
20:24(UTC): A Second Binance Hot Wallet Transfers Assets
Twenty-four seconds after the first sweep, “Binance 16” transferred the following assets to the same receiving address:
- 28,005.6 ETH;
- 55.7 million USDT;
- 25.9 million RLUSD;
- 84.5 WBTC;
- Several other tokens.
No EIP-7702 delegation was identified on this wallet. The assets were transferred through ordinary transactions signed by the wallet itself.
20:25–20:36(UTC): Abnormal Transfers Appear Across Multiple Blockchains
Over the following 12 minutes, abnormal transactions appeared across several Binance-linked hot wallets on Ethereum, Bitcoin, Tron, Optimism, Arbitrum, and Avalanche.
Publicly reported transfers included:
- Optimism: approximately 44.2 million OP;
- Arbitrum: approximately 74.6 million ARB and 8,426 ETH;
- Avalanche: approximately 1.81 million AVAX and 8.41 million USDT;
- Bitcoin: a large quantity of BTC sent to attacker-linked addresses;
- Tron: large stablecoin transfers.
Blockaid estimated that at least $5.5 billion moved abnormally across multiple networks. The attacker address cluster tracked by Arkham was at one point valued at approximately $5.78 billion.
20:41(UTC): Approximately $823 Million in USDC Transferred
The attacker then used the still-delegated Binance 14 wallet to interact with a Binance-linked smart account under its control.
Two additional transfers were made:
- Approximately 780 million USDC;
- Approximately 43 million USDC.
The two transfers totaled approximately $823 million.
20:58–21:01(UTC): The Attacker Uses Aave to Convert Assets
After the transfers, the attacker began distributing the assets across multiple new wallets and interacting with decentralized exchanges, aggregators, bridges, and lending protocols.
One associated address supplied 60 million USDT to Aave V3 and borrowed 19,762 WETH, worth approximately $44.6 million at the time.
The attacker also converted tokens including UNI, LINK, and AAVE into ETH. Aave Risk Team Report
21:16(UTC): Binance Issues Its First Public Response
At approximately 21:16(UTC), Binance said through its official channels that its teams were aware of a potential security incident and had launched an urgent investigation. The exchange emphasized that user funds were safe.
CZ later said on X that the incident appeared to be a hack targeting Binance. Although he is no longer responsible for the exchange’s daily management, he said he expected all user funds to be fully covered.
Binance co-founder Yi He also stated that the platform would cover all losses resulting from the incident. We
After 21:42(UTC): Stablecoin Issuers Begin Freezing Assets
Binance subsequently worked with stablecoin issuers, blockchain projects, security firms, and law enforcement agencies to freeze assets controlled by the attacker.
Publicly disclosed actions include:
- Tether froze approximately 1.567 billion USDT;
- Circle froze approximately 800 million to 823 million USDC;
- Ripple froze approximately $200 million in related assets;
- World Liberty Financial froze approximately $27 million in USD1;
- The Arbitrum Security Council restricted approximately $30.5 million in associated assets;
- Additional stablecoins and tokens were also restricted.
Binance’s latest statement places the total frozen on-chain amount at approximately $3 billion.
Freezing prevents the attacker from continuing to transfer or use the affected assets. However, returning those assets may still require cooperation among issuers, law enforcement agencies, and judicial authorities.
21:44(UTC): The Attacker Sweeps Binance 14 Again
Because the malicious delegation on Binance 14 had not yet been revoked, assets deposited into the address after the first sweep remained accessible to the attacker.
At approximately 21:44(UTC), the attacker again transferred assets from Binance 14, including:
- Approximately 200 million USDT;
- Thirteen additional tokens.
Public on-chain records indicate that Binance subsequently revoked the EIP-7702 authorization on the affected address.
Binance Publishes Its Preliminary Findings
In its latest official response, Binance said its preliminary investigation indicated that:
- A DevOps engineer’s laptop may have been compromised;
- The attacker gained access to a related service container;
- Unauthorized withdrawal transactions were submitted;
- No evidence of a direct wallet private-key leak has been found;
- The estimated total impact is approximately $6.3 billion;
- Around $3 billion in affected assets has been frozen on-chain.
This suggests that EIP-7702 was the on-chain method used to control Binance 14, while the initial point of entry may have involved Binance’s internal operations equipment and service environment.
Binance said it would release a detailed technical post-mortem after the investigation is completed and the facts have been fully verified. Official Binance Response
Actions Taken by Binance
Following the incident, Binance has:
- Temporarily suspended deposits and withdrawals;
- Revoked the malicious authorization on the affected address;
- Conducted security checks on wallets and related systems;
- Worked with stablecoin issuers and blockchain projects to freeze assets;
- Engaged blockchain intelligence firms to trace the funds;
- Contacted law enforcement agencies to investigate the attackers;
- Committed to covering all losses using the SAFU fund and company funds;
- Announced plans to publish an updated Proof of Reserves after remediation.
Does $6.3 Billion Represent the Final Loss?
No.
The $6.3 billion figure represents Binance’s current estimate of the incident’s total impact. It includes abnormal transfers involving multiple networks, hot wallets, and digital assets.
Approximately $3 billion has already been frozen, while the remaining assets continue to be traced. The final unrecoverable net loss has not yet been determined.
Measured by total impact, the incident has surpassed the approximately $1.5 billion Bybit hack in 2025, making it the largest single security incident in the history of the cryptocurrency industry.
Current Status
As of publication:
- Binance user account balances have not been reduced;
- Binance has committed to covering all losses;
- Deposits and withdrawals remain suspended or subject to security checks;
- Approximately $3 billion in affected assets has been frozen;
- The identity of the attacker has not been confirmed;
- The final recovery amount remains unknown;
- A complete technical post-mortem has not yet been published;
- An updated Proof of Reserves is still pending.
This article is based on Binance’s official statement, publicly available on-chain transaction records, and current information from Blockaid, Arkham, the Aave risk team, and other sources. The incident remains under investigation, and the figures may continue to change.
Responses